Cybersecurity, architecture and resilience for complex organizations

SAOG Cyber helps organizations enhance cybersecurity, governance, risk and compliance, security architecture, and OT resilience. With expertise in aerospace, defence, and manufacturing, we translate complex risks and requirements into practical solutions that safeguard operations and advance business goals.

Qualifications

Certifications and designations

Our CMMC qualifications, verifiable on The Cyber AB marketplace

Certification

ISACA

Lead CMMC Certified Assessor (LCCA)

The LCCA conducts official CMMC Level 2 certification assessments. As a CCA, he evaluates evidence, validates security controls, conducts interviews, and determines whether organizations handling CUI meet CMMC Level 2 requirements.

Designation

The Cyber AB

Registered Practitioner Advanced (RPA)

The RPA is a CMMC-designated expert to support organizations in implementing CMMC Level 2 practices across all 14 security domains (AC through SI). Services include CUI scoping, control implementation, assessment support, documentation drafting, and correction of SSP and POA&M deficiencies.

Insights

Insights for stronger, more resilient organizations

We provide practical analysis on cybersecurity, governance, security architecture, OT, and risk to help organizations make informed decisions and protect critical operations.

CPCSC

Navigating CMMC 2.0 and CPCSC: a strategic guide for defence SMEs

These two programs are important for Canadian suppliers in North American supply chains. While CMMC and CPCSC share similar objectives, they are separate programs with different reference standards, assessment methods, and contractual requirements.
Services

What we do

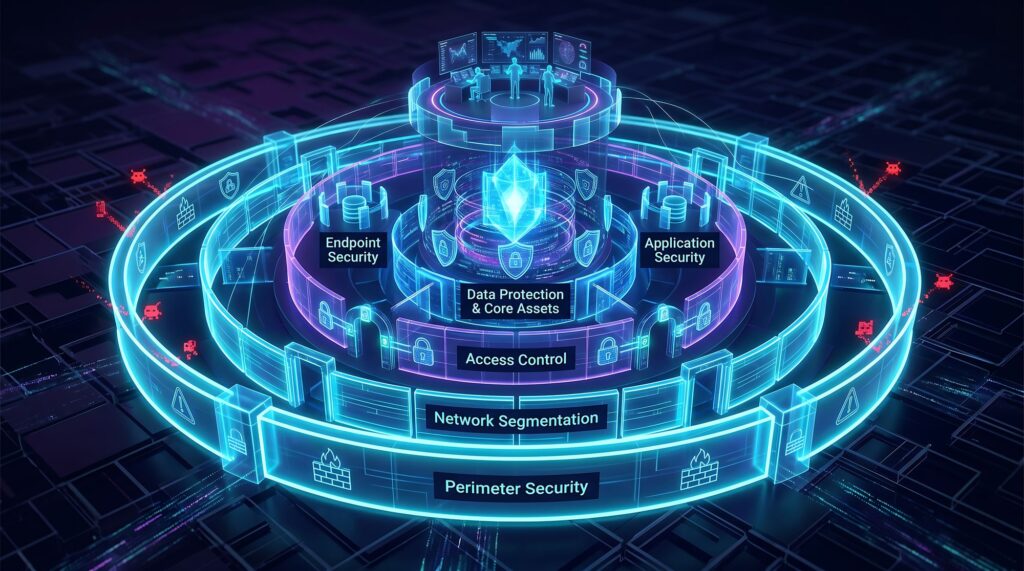
SAOG Cyber supports organizations in managing cyber risk and strengthening operational resilience, from governance and security architecture to OT protection and compliance.

Approach

A clear path from uncertainty to evidence

We follow a disciplined five-step process. Each phase builds the foundation for the next, ending with assessment-ready proof.

Define

We validate the scope of your engagement, confirming which assets fall within the assessment boundary

Assess

We measure your current security posture against the required controls


Prioritize

We sequence the work so the most critical gaps close first


Implement

We build the technical controls and documentation your assessment demands


Prepare

We organize your evidence so you face the assessor with confidence


Why SAOG Cyber

Cybersecurity expertise for critical industries

We understand the cybersecurity, GRC, and operational technology challenges that organizations encounter. Our bilingual specialists turn technical, operational, contractual, and regulatory requirements into practical steps to strengthen resilience, protect critical operations, and ensure compliance.